The EU Artificial Intelligence Act entered into force on 1 August 2024 and has applied in stages since. On 2 August 2026 the majority of its rules started to apply, and enforcement began for the rules already in application. The obligations for high-risk AI systems are the important exception: they now apply later, and on different dates depending on the type of system.
Updated 29 October 2026. An earlier version of this article said the Annex III high-risk obligations would become enforceable on 2 August 2026. That is no longer correct: the AI Omnibus moved them to 2 December 2027. The dates below follow the European Commission's published timeline as of October 2026. This article is general information, not legal advice.
The detail that still catches UK firms off guard is reach. The Act is not confined to companies based in the EU. It can apply when an AI system is placed on the EU market or when its output is used inside the bloc. A UK firm with EU clients, EU staff or EU end users can be in scope.
Key dates
These are the main dates on the European Commission's timeline as of October 2026.
- 2 February 2025: prohibited practices and AI literacy obligations apply.
- 2 August 2025: obligations for providers of general-purpose AI models apply, and EU-level governance is in place.
- 2 August 2026: most of the Act's rules apply, including the Article 50 transparency rules, and enforcement starts at national and EU level for the rules already in application.
- 2 December 2026: new prohibitions apply, and a transition deadline falls for certain providers under Article 50(2).
- 2 December 2027: obligations for high-risk AI systems in Annex III apply.
- 2 August 2028: obligations for high-risk AI embedded in products covered by Annex I apply.
Does the Act apply to you?
Start with three questions. Do you place an AI system or a general-purpose AI model on the EU market? Do you use AI whose output is used by people in the EU? Do you deploy AI inside an EU operation? A yes to any of these can bring you into scope.
For a UK financial firm, law firm or healthcare provider with European clients or offices, some part of the business may be in scope, depending on the systems it uses and where their output is used. The Act follows the market and the output, not only the registered address. "We are a UK firm, so it does not apply" is the same assumption many made about GDPR. Confirm your position with your legal advisers rather than assuming it.
The risk categories
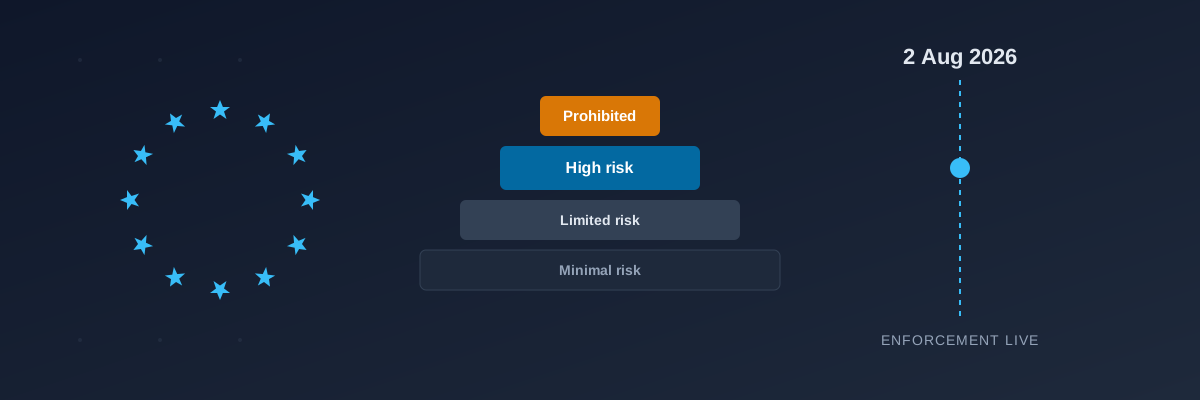
The Act matches obligations to risk.
Prohibited practices. A defined set of uses is banned, such as social scoring and certain biometric categorisation. These prohibitions have applied since 2 February 2025, and new prohibitions on AI systems that generate non-consensual sexual deepfakes or child sexual abuse material apply from 2 December 2026.
High risk. The most demanding category. Annex III lists use cases in sensitive areas, including employment, creditworthiness and biometrics. Annex I covers AI embedded in products already regulated by EU product legislation. High-risk systems carry obligations on risk management, data quality, documentation, logging, human oversight and accuracy. They apply from 2 December 2027 for Annex III and from 2 August 2028 for Annex I.
Transparency risk. Duties such as telling people when they are interacting with an AI system and marking synthetic content. The Article 50 transparency rules have applied since 2 August 2026, with a transition to 2 December 2026 for certain providers of systems already on the market.
Minimal risk. Most everyday AI, which carries no specific obligations under the Act beyond those that apply generally.
Separate rules cover general-purpose AI models, the foundation models behind tools such as ChatGPT, Claude and Gemini. Their providers have had transparency, documentation and copyright obligations since 2 August 2025, with additional obligations for models with systemic risk.
What changed in 2026
Two developments matter.
The AI Omnibus. This amending regulation entered into force on 27 July 2026. Among other changes, it moved the high-risk dates to 2 December 2027 (Annex III) and 2 August 2028 (Annex I), added the new prohibitions that apply from 2 December 2026, and simplified the AI literacy requirement for companies.
2 August 2026. According to the Commission, the majority of the Act's rules started to apply on this date, and enforcement started at national and EU level for the rules already in application: the general-purpose AI model obligations, the prohibitions, the transparency rules and AI literacy. Regulators can now investigate and fine for breaches of those rules.
The Commission states that prohibited practices can attract fines of up to €35 million or 7% of total worldwide annual turnover, and breaches of the general-purpose AI model obligations up to €15 million or 3%. As with GDPR, these are ceilings, not standard penalties.
What to do now
The later high-risk dates give firms more time. They do not remove the work, and the order still matters.
Build an AI inventory. You cannot classify what you cannot see. Many firms find they have no reliable picture of which AI tools staff use, which are sanctioned and what data each can reach. A discovery exercise such as an AI data leakage assessment produces that baseline, including unsanctioned and embedded AI that rarely appears on a software register.
Classify each use. Sort each system into prohibited, high risk (Annex III or Annex I), transparency or minimal. The category decides which date applies. This is also where firms find uses they did not realise were high risk, such as AI in hiring or credit decisions.
Check what already applies. Prohibitions, AI literacy, transparency and the general-purpose AI model rules are already in application and under enforcement. Confirm that nothing you use falls into a prohibited practice, and that people are told when they are dealing with an AI system where the transparency rules require it.
Document and evidence high-risk systems. High-risk systems need technical documentation, logging and records of human oversight. Building that evidence trail before the 2027 and 2028 dates is easier than assembling it under a regulator's timeline. It connects directly to an AI governance framework for the enterprise that keeps the documentation current.
Put human oversight in place. For high-risk systems, the Act expects meaningful human oversight. Decide who is accountable, what they can see and when they can intervene.
How this sits alongside the FCA
UK financial firms also answer to UK regulators. The FCA says it does not plan to introduce extra regulations for AI. Instead it relies on existing frameworks, such as the Consumer Duty, and its rules emphasise accountability for senior managers, for example under the Senior Managers and Certification Regime. Our CISO guide to the EU AI Act looks at security tooling, and our article on an AI audit trail for compliance covers recording how AI-assisted decisions are made.
In our view, the groundwork overlaps: an inventory of AI use, a record of how decisions are overseen and documentation a third party can follow are useful under both regimes. That is a practical observation, not a statement of what either regulator requires.
Sources
- European Commission, Regulatory framework for AI (application timeline and AI Omnibus status, updated 19 October 2026)
- European Commission, Enforcement of the AI Act (enforcement dates and fine ceilings, updated 20 October 2026)
- European Commission, AI Omnibus enters into force (27 July 2026)
- Financial Conduct Authority, AI and the FCA: our approach (last updated 2 October 2026)
- AI Act Service Desk, Timeline for the implementation of the EU AI Act
The consolidated legal text on EUR-Lex is the authoritative source for the exact obligations.